
Software Assurance
Accountable for your software in production, whoever wrote it
We assess, assure, run and improve business-critical software, whether your team, AI tools, another agency or we wrote it. When a check finds something, the same team can fix it, so there is no second supplier to bring in.
Why software assurance matters now
AI tools can now write most of the code in a new system, and in ours they do. That makes software faster to produce. It does not tell you whether the result is secure, does what was asked for, or will keep running when the person who built it moves on.
Software assurance answers those questions with evidence. We check software against recognised standards, test it, run it under an agreed service level, and record what was checked. In our own delivery, 91.6% of our code is AI-authored, and 100% of it is reviewed by senior engineers and validated by ISTQB-qualified QA. We apply the same standard to code we did not write.
Assess, assure, operate and evolve
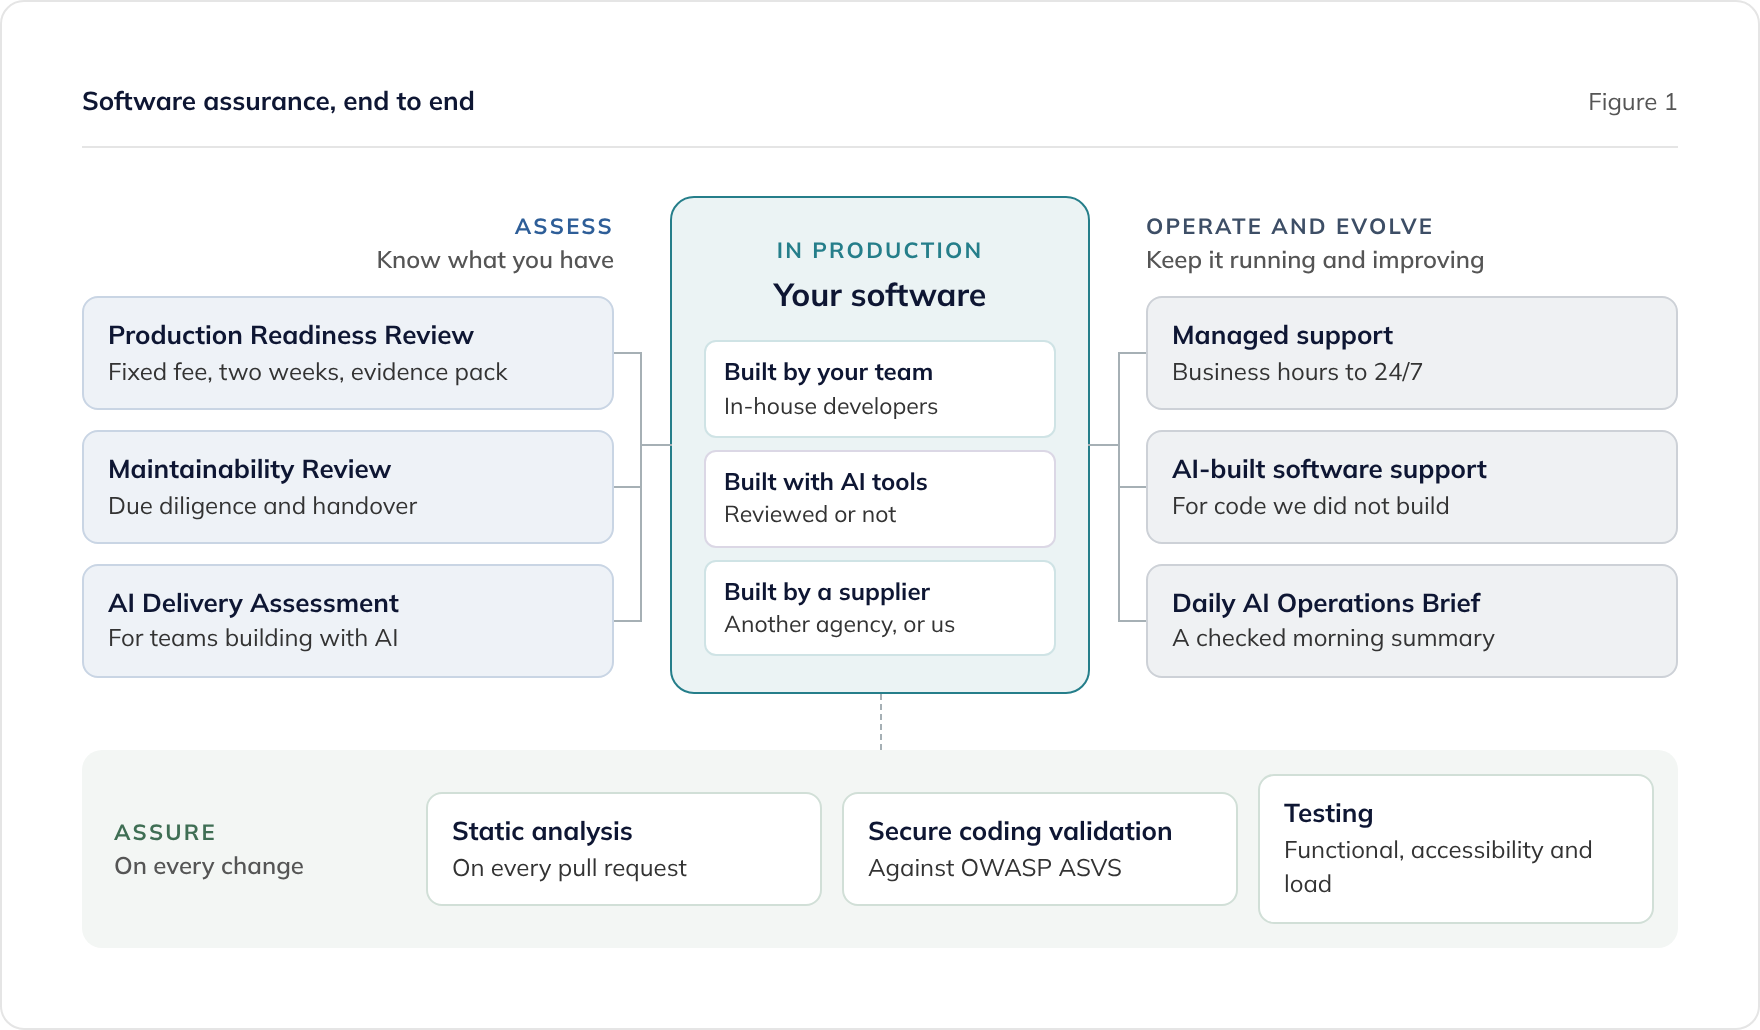
Each service answers a different question about a system in production. Most clients start with an assessment, then move to support, with the same checks running on every change.
Find out what you have
A fixed scope and a written result, so you know the risks before anyone commits to support or a rebuild.
£5,500 fixed, two weeks
Production Readiness Review
Static analysis, secure coding validation against OWASP ASVS, a dependency audit, an accessibility scan and a test coverage baseline, delivered as an evidence pack you can share.
Fixed price, scoped on the first call
Maintainability Review
What a codebase is worth and what it will cost to keep, for acquisitions, investments, supplier exits and handovers.
£9,500 fixed, three weeks
AI Delivery Assessment
For engineering teams adopting AI tools: a baseline of your delivery metrics, benchmarked against our published AI Velocity Report data, with a 90-day roadmap.
The checks every change passes
Our QA practice, applied in our delivery and managed support work, to our own code and to code we did not build.
Static code analysis
Expert-led secure coding validation
Functional and regression testing
Accessibility testing
Load, stress and soak testing
Penetration testing, through a specialist
Keep it running
SLA-backed support from our UK team, with round-the-clock cover through our partner Just After Midnight where you need it.
From £1,590 a month
Managed Application Support
Monitoring, incident response, bug fixes and security updates under an agreed service level, from business hours to 24/7.
From £2,450 a month
Managed Support for AI-Built Software
This service covers AI-generated codebases we did not build, starting with a Production Readiness Review.
Part of managed support
Daily AI Operations Brief
A morning AI summary of telemetry, alerts and tickets on your live system, with an engineer checking every finding.
On our top service level, we respond to priority 1 incidents within one to two hours. Onboarding typically takes one to eight weeks, depending on how complex the system is.
Take over, stabilise and improve
When the people who built the software have gone, or it was never built to be supported.
For AI-built apps in trouble
Vibe Coding Rescue
Stabilise an AI-generated application that is already failing in production, then decide whether to rescue or rebuild.
When the builder has gone
Inherited Codebase Takeover
Take over a system whose developer or supplier has left: secure access, document what exists and put it under support.
For established estates
Development Partner Transition
A structured move of a business-critical estate from your current development partner to us, with knowledge transfer and shadow support.
Stabilise, refactor or rebuild
Prototype to Production
Turn a working prototype built with AI tools into software you can depend on, starting with an assessment.
How we hold ourselves to the same standard
We develop software under an ISO 27001:2022-certified information security management system, which governs our secure development lifecycle, change control and supplier management. We are also accredited to Cyber Essentials Plus. Code is deployed into client-managed cloud environments, and runtime security in those environments remains the client's responsibility, in line with our defined ISMS scope.
We publish how we build every quarter in the AI Velocity Report, including the checks every AI-written change passes and what a measured change actually took.
Seen enough? Let's talk through your requirements.
Book a free consultationFrequently asked questions
What is software assurance?
Software assurance is the work that gives you confidence a system is safe to depend on: checking the code against recognised standards, testing it, running it under an agreed service level, and producing evidence of what was checked. For us it also includes fixing what the checks find, so you do not need a second supplier.
Do you only assure software you built?
No. We review and support code we did not build as well as our own, whether your team, AI tools or another agency wrote it. For AI-generated codebases we did not build, the Production Readiness Review is the first step before ongoing support.
Where should we start?
It depends on the question you need answered. If you need to know whether software is safe to put in front of users, or a buyer has asked for security evidence, start with a Production Readiness Review. For due diligence or a supplier exit, start with a Maintainability Review. If your own engineers build with AI and you want to know whether it is working, start with the AI Delivery Assessment.
Do you carry out penetration testing?
No. Our secure coding suite is built from the findings of penetration tests on previous projects, so issues that real tests have found are checked for on every review. If a customer or insurer needs a penetration test, commission it from a CREST-accredited tester, and we can fix its findings alongside ours. Our guide to penetration tests and production readiness reviews explains which to do first.
Can you guarantee our software is secure?
No. Nobody can guarantee that a system is secure. What we do is describe exactly what we checked, against which standard, and what was out of scope, then fix what we find and keep checking every change. Every review report lists the requirements we checked and the ones we did not.
What does it cost?
The Production Readiness Review is £5,500, fixed, over two weeks. The AI Delivery Assessment is £9,500, fixed, over three weeks. Managed support starts from £1,590 a month for conventional codebases and from £2,450 a month for AI-generated codebases we did not build. See our pricing page for current figures.
Go deeper
What Assured AI Development Looks Like
The four properties of assured AI development, with our own published delivery data.
Who Is Accountable When AI Writes the Code?
How accountability splits between AI vendors, suppliers and your organisation.
Penetration Test or Readiness Review?
What each finds, which to do first, and how to choose a tester.
Production Readiness Checklist
45 checks mapped to OWASP ASVS and Cyber Essentials Plus, with an interactive version.
Security Questionnaires for AI-Built Products
How to answer the secure development questions buyers ask.
Governing Software Your Staff Build with AI
A proportionate policy for tools built by staff, and when they need support.
See how AI is changing how we build software
Our quarterly AI Velocity Report tracks real delivery metrics from live projects: how much of our code is AI-authored, how delivery timelines compare to baseline, and which tools are making a measurable difference. No marketing spin, just honest data from a team that builds software every day.
Read the latest AI Velocity ReportMake someone accountable for your software
Book a consultation and we will tell you which assessment fits, what it costs, and what you get at the end of it.
Book a consultationor call 01202 006729