
Maintainability Review & Due Diligence
Know exactly what you're getting before you commit
Whether you're acquiring a product, evaluating a vendor's work, or assessing your own technical debt, we provide an independent, expert review of the codebase. No surprises after the deal is done.
Common scenarios for a maintainability review
Pre-acquisition due diligence
Vendor assessment or agency exit
Internal health check
Pre-investment review
A thorough review across six critical areas
Every review is tailored to your situation, but these are the areas we always cover.
Code quality and architecture
We assess code structure, separation of concerns, naming conventions, duplication, and overall architectural coherence. Is this codebase one that competent engineers can maintain and extend?
Security posture
Authentication, authorisation, data handling, secret management, dependency vulnerabilities, and compliance with standards like OWASP Top 10. We flag issues by severity.
Test coverage and CI/CD
What's tested, what isn't, and how code gets to production. We review pipelines, deployment practices, rollback capabilities, and environment management.
Infrastructure and scalability
Hosting configuration, database design, caching strategy, and whether the system can handle growth. We assess cost efficiency and identify single points of failure.
Documentation and knowledge risk
Is the system documented? Could a new team pick this up? We identify bus factor risks and knowledge gaps that could become expensive problems.
Dependency and licence risk
Third-party libraries, framework versions, end-of-life dependencies, and open-source licence compliance. We flag anything that creates legal or maintenance risk.
Security review of an outdated web application
We are often asked to review an older web application that still runs part of the business but has not been patched or upgraded for years. The review covers the same six areas as any other, with extra weight on the risks that build up in software nobody is actively maintaining:
- Frameworks and runtimes that are out of vendor support and no longer receive security fixes
- Third-party dependencies with published vulnerabilities
- Authentication, session handling, and how secrets and connection strings are stored
- Common web vulnerabilities against the OWASP Top 10
- Hosting configuration, certificates, and backups
Each finding is rated by severity, so you can see what needs fixing now and what can wait for a planned upgrade. A code-level review is not a penetration test. Where you also need one, we recommend commissioning it from a CREST-accredited tester, and we can remediate its findings alongside ours.
Remediation can run as a one-off project or move into legacy application support, where patching and dependency updates continue on a schedule. We hold Cyber Essentials Plus and ISO 27001 certification ourselves. Our guide to keeping supported software secure explains how we handle vulnerabilities once a system is in support.
From code audit to SLA-backed support
Many reviews are the first step in changing supplier. When you are moving an application away from the agency that built it, we audit the code first so that you, and we, know what is being taken on before any support commitment is made.
If you then move support to us, the review findings become the stabilisation plan for onboarding. We set up monitoring, runbooks, and CI/CD access, and agree response and resolution targets per severity level before the SLA starts. Managed application support starts from £1,590 per month and scales with scope, SLA tier, and team size.
For a business-critical estate with an outgoing supplier still in contract, our development partner transition service adds structured knowledge transfer and parallel running. Our guide to changing application support supplier sets out the full sequence.
From review to remediation
How a maintainability review progresses from initial scoping to actionable recommendations.
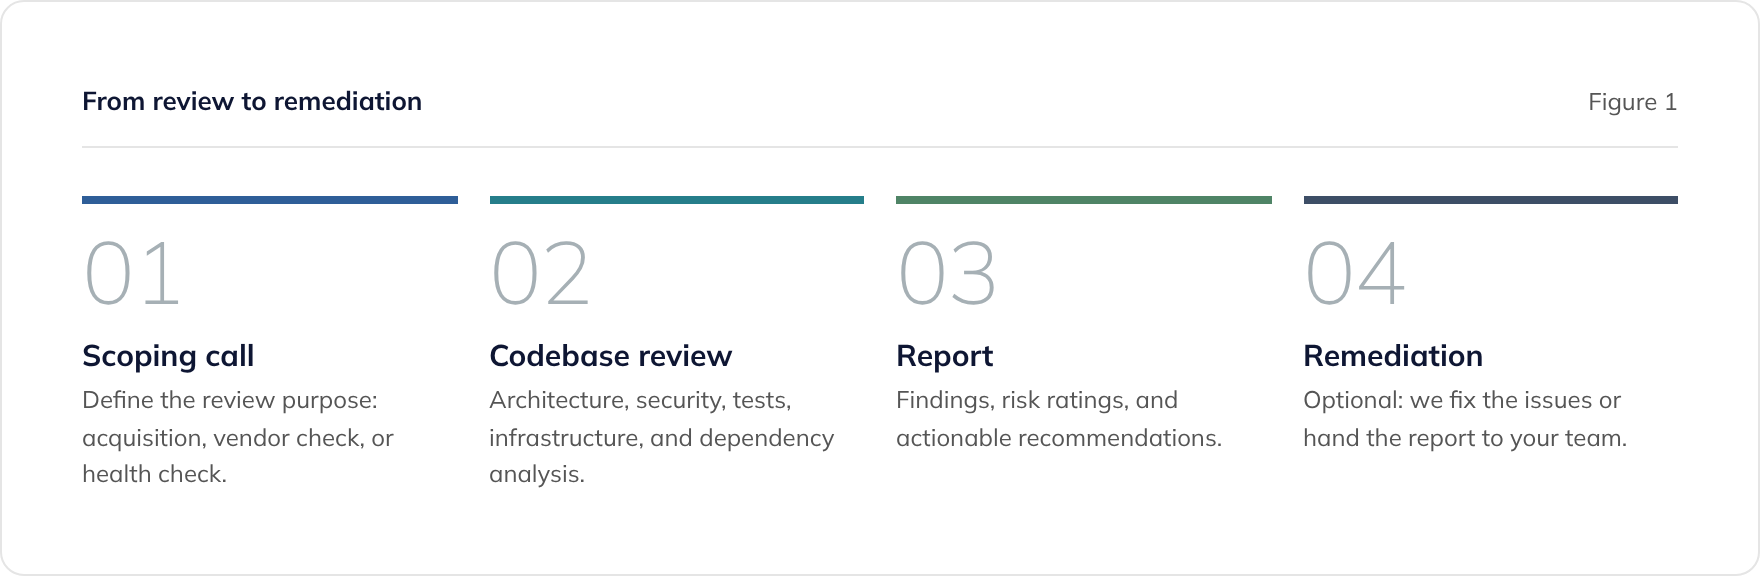
From scoping to actionable report
A structured process designed to give you the information you need to make confident decisions.
-
Scoping call
30 minutesWe discuss what you need the review for: acquisition, vendor check, internal health check, or investment. This helps us tailor the review to the questions that matter most to you.
-
Codebase review
3-10 daysOur senior engineers review the codebase, infrastructure, and deployment setup. The depth and duration depends on the size of the system and the scope agreed in step one.
We use a combination of manual review and automated tooling to cover:
- Architecture and code quality
- Security vulnerabilities
- Test coverage and CI/CD maturity
- Dependency and licence risks
- Infrastructure configuration
-
Report and recommendations
You receive a detailed written report covering findings, risk ratings, and actionable recommendations. We then walk you through the findings in a presentation, answer questions, and discuss next steps.
The report is yours to share with stakeholders, investors, or legal advisors as needed.
"Talk Think Do were very strategic and intelligent in the way that they set it up right from the beginning, allowing us to make leaps forward."
Bill Mills
CEO, Explore Learning
Seen enough? Let's talk through your requirements.
Book a free consultationFrequently asked questions
How long does a review take?
Typically 3-10 working days for the review itself, depending on the size and complexity of the codebase. You'll receive the report within a few days of the review completing. The scoping call and report walkthrough are scheduled around your availability.
What access do you need?
Read-only access to the source code repository, plus access to infrastructure configuration and CI/CD pipelines where possible. We can work with limited access if needed (for example, during pre-acquisition due diligence where full access isn't yet available).
Can you audit our code and then support it under an SLA?
Yes. This is a common route when an organisation is moving an application away from the agency that built it. The review comes first, so you know what you are inheriting. If you then move support to us, the findings become the stabilisation plan for onboarding, and SLA terms are agreed once we understand the system. Managed support starts from £1,590 per month and scales with scope, SLA tier, and team size. See our development partner transition service for the full handover from an outgoing supplier.
Can you carry out a security review of an outdated web application?
Yes. Security posture is one of the six areas every review covers, and for older applications we focus on unsupported frameworks, vulnerable dependencies, authentication, secret handling, and the OWASP Top 10. A code-level review is not a penetration test. If you also need one, commission it from a CREST-accredited tester; we can remediate its findings alongside our own.
Can you sign an NDA?
Yes. We routinely sign NDAs for due diligence and vendor assessment work. We can use your standard NDA or provide ours.
What do we get at the end?
A detailed written report covering all review areas, with findings rated by severity and business impact. Each finding includes a clear recommendation. You also get a walkthrough session where we present the findings and answer questions.
Can you fix the issues you find?
Yes. If the review identifies issues that need addressing, we can provide a proposal for remediation work, either as a standalone engagement or as part of an ongoing managed support arrangement.
How much does a review cost?
Reviews are fixed-price engagements scoped during the initial call. Cost depends on the size of the codebase and depth of review required. Book a consultation for a quote.
See how AI is changing how we build software
Our quarterly AI Velocity Report tracks real delivery metrics from live projects: how much of our code is AI-authored, how delivery timelines compare to baseline, and which tools are making a measurable difference. No marketing spin, just honest data from a team that builds software every day.
Read the latest AI Velocity ReportMake informed decisions about software you depend on
Book a free consultation to discuss what you need reviewed and why. We'll scope the engagement, provide a fixed-price quote, and give you an honest assessment of whether a review is even necessary.
Book a free consultationor call 01202 006729