
Technical Due Diligence
Know what the software is worth before you buy or invest
Our senior engineers assess the architecture, code, security, infrastructure and delivery practice behind a business you are acquiring or investing in. You get a written report, rated by risk, that you can share with your investors and legal advisers.
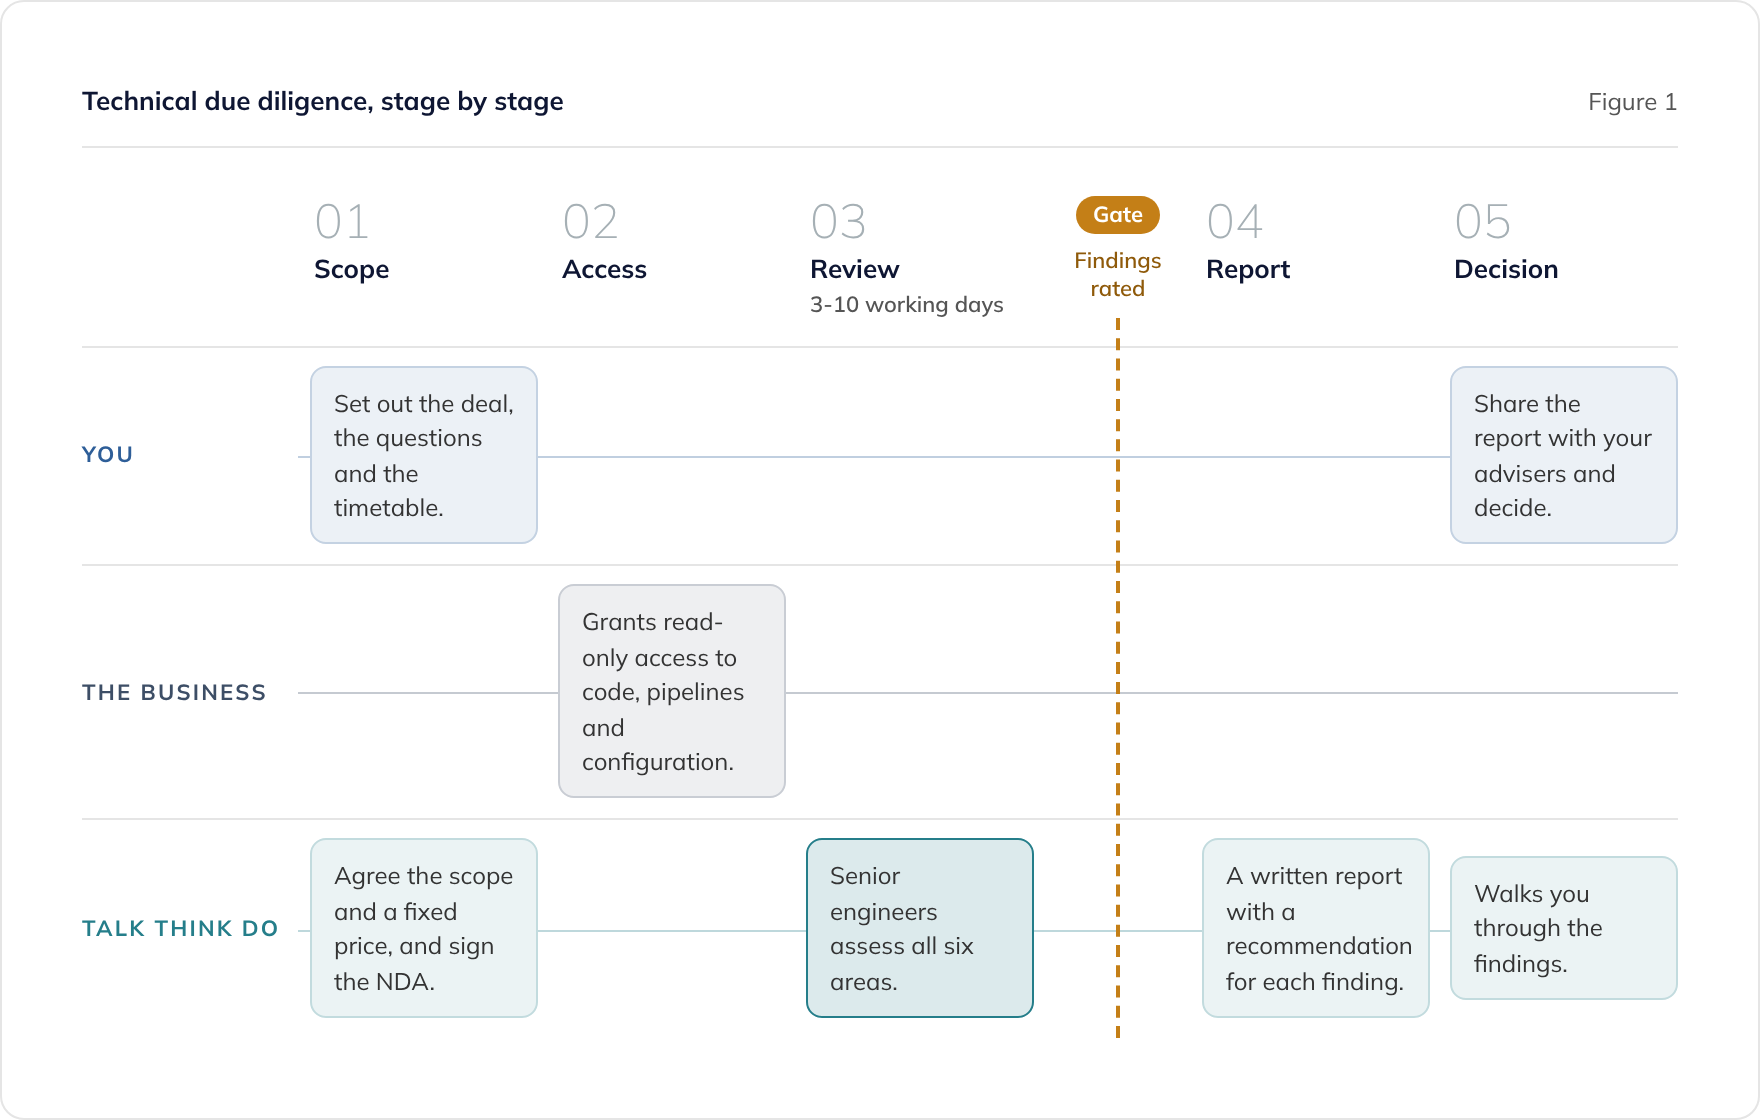
Technical due diligence from Talk Think Do is an independent assessment of a business's software before you acquire it, invest in it or come to depend on it. The review typically takes 3-10 working days, works with the limited access usual before a deal completes, and ends in a report rated by risk. It is fixed price, quoted after a short scoping call.
When to commission technical due diligence
Each of these is a point where a decision is hard to reverse once it is made.
Before an acquisition
Before an investment
Before you depend on a system
What technical due diligence covers
Six areas, each with findings rated by severity and business impact.
Architecture and code quality
Security posture
Infrastructure, scale and running cost
Delivery practice
Knowledge and team risk
Dependency and licence risk
A code-level review is not a penetration test. If the deal needs one, commission it from a CREST-accredited tester. We also go deeper on architecture on its own, through our architecture assurance service.
Who does what during the review
Most of the work is ours. You set the questions and the timetable, and the business being assessed gives us access.
Due diligence we have carried out
We have carried out technical due diligence for clients before. For CalMac Ferries, operator of the UK's largest ferry network, we carried out independent technical due diligence on another core system alongside our managed support of their integration platform. The work gave CalMac recommendations for improvement and supported decisions on where to invest.
If the deal goes ahead, the findings can become the plan for what comes next. We can fix what the review finds, take on the system under managed support, or hand the findings to the team that will.
Seen enough? Let's talk through your requirements.
Book a free consultationFrequently asked questions
What is technical due diligence?
Technical due diligence is an independent assessment of a business's software before you buy it, invest in it or come to depend on it. It tells you what the software is worth, what it will cost to maintain, and which risks could affect the deal. We cover architecture, code quality, security, infrastructure, delivery practice, knowledge risk and third-party dependencies.
How is this different from a Maintainability Review?
The review areas overlap, but the audience differs. Technical due diligence answers the questions an acquirer or investor needs settled before a deal, and the report is written to be shared with your advisers. A Maintainability Review is for an organisation that already owns a system and needs to decide what to do with it, such as changing supplier or taking it in-house.
How long does it take?
The review itself typically takes 3-10 working days, depending on the size and complexity of the system. You receive the report within a few days of the review finishing. We fit the scoping call and the walkthrough around your deal timetable.
Can you work with limited access before the deal completes?
Yes. Ideally we have read-only access to the source code, the infrastructure configuration and the build pipelines. Before completion that is often not possible, so we agree on the scoping call what we can see and state in the report what we could not check.
Can you sign an NDA?
Yes. We routinely sign NDAs for due diligence work, and we can use your standard NDA or provide ours.
Do you assess AI-generated code?
Yes. We look at how AI coding tools were used, whether a person reviewed and was accountable for what they produced, and what that means for maintenance and security. We write and review AI-generated code every day in our own delivery, so we know where it tends to go wrong.
Do you advise on intellectual property?
No. We are engineers, not lawyers. We identify the third-party code, open-source licences and authorship questions in a codebase, and flag anything your legal advisers should look at. Our guide to IP licensing and source code handover covers the contractual side.
What does it cost?
Technical due diligence is fixed price, quoted after a short scoping call, because the cost depends on the size of the system and how deep the review needs to go. Book a consultation for a quote.
Go deeper
IP Licensing and Source Code Handover
What a software contract should say about ownership, licences and handover.
Who Owns AI-Written Code?
What CTOs, developers and procurement teams need to know about AI-generated code.
Do You Actually Own Your Software?
A control checklist for the code, accounts and infrastructure behind a product.
Security and Continuity Evidence
The evidence enterprise buyers ask software vendors for, and how to provide it.
What Assured AI Development Looks Like
The four properties of assured AI development, with our own published delivery data.
Penetration Test or Readiness Review?
What each finds, which to do first, and how to choose a tester.
Technical due diligence is one part of our software assurance services. If you already own the system and need to decide what to do with it, start with a Maintainability Review.
See how AI is changing how we build software
Our quarterly AI Velocity Report tracks real delivery metrics from live projects: how much of our code is AI-authored, how delivery timelines compare to baseline, and which tools are making a measurable difference. No marketing spin, just honest data from a team that builds software every day.
Read the latest AI Velocity ReportFind out what you are buying
Book a consultation and we will tell you what a review would cover for your deal, how long it would take, and what it would cost.
Book a consultationor call 01202 006729